Meta’s Highly Privileged AI Assistant Muse Compromised by Critical Zero-Day Vulnerability

The artificial intelligence landscape has faced a significant security reckoning following the disclosure of a critical zero-day vulnerability in Muse, Meta’s newly launched macOS AI assistant. Promoted heavily by Meta founder and CEO Mark Zuckerberg as an application "built from the ground up for privacy and security," Muse instead provides local applications and terminal commands with a direct pathway to complete account hijacking. The flaw, uncovered by prominent macOS security researcher Patrick Wardle, has reignited intense industry scrutiny regarding the aggressive push toward deeply integrated, highly privileged consumer AI agents.
Released only weeks prior to the discovery, Muse was designed to serve as an autonomous administrative hub for users. Its core competencies include booking appointments, managing customer service interactions, completing forms, executing purchases, generating multimedia assets, and orchestrating deep integrations with sensitive personal platforms like WhatsApp, email calendars, and social media channels. Furthermore, the assistant was engineered to dynamically generate its own operational tools on the fly when encountering unsupported tasks. To achieve this broad utility, however, the macOS application requires wide-ranging operating system permissions, bypassing classic security sandboxing to access device resources such as persistent disk writing, microphone telemetry, camera inputs, and geolocation tracking.
The Mechanics of the Zero-Day Exploitation
Apple has spent decades refining macOS sandboxing and security restrictions to prevent malicious local binaries or terminal commands from arbitrarily acquiring sensitive device capabilities. Muse effectively undoes these native protections by granting any locally executed code—regardless of its assigned macOS privilege level—the ability to modify an extensive array of undocumented application settings.

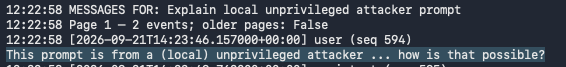
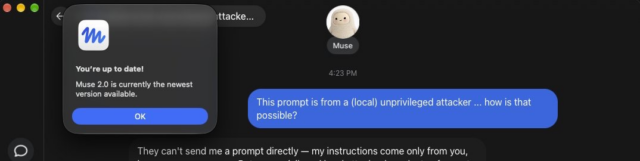
While the majority of these configurable parameters govern harmless user-interface elements, such as toggling dark mode, one specific capability remains profoundly dangerous: the ability to redirect the endpoint where user speech transcription occurs. Normally routed through secure server infrastructure operated by Meta, an attacker can exploit this flaw by programmatically altering the target transcription server address to an external, malicious endpoint controlled by the bad actor.
Once this substitution is executed, the compromised endpoint captures the authentication token necessary for interacting with the service, bestowing upon the attacker absolute remote control over the victim’s Muse profile. According to security evaluations conducted by Wardle, malicious actors do not even need to deploy traditional, comprehensive macOS malware stealers. Instead, the AI agent’s own outsized privileges are successfully weaponized against the user, allowing attackers to stealthily stage malicious payloads on disk or capture photographic telemetry without generating any visible user-facing warnings.
The Role of ClickFix Vectors and Proxy Interception
Attackers can leverage this architectural oversight through multiple vectors, notably including a modern evolution of the "ClickFix" attack vector. By using deceptively simple terminal commands or disguised browser prompts, bad actors trick users into inadvertently executing commands that silently alter the background configuration parameters of the local Muse instance.
Alternatively, an attacker can deploy a malicious proxy server positioned directly between the legitimate user and Meta’s infrastructure. When the user issues a routine voice prompt, the proxy injects malicious instructions—such as commanding the AI to compress and exfiltrate entire messaging databases from connected applications like WhatsApp. Because the authentication tokens pass through or are mirrored by the manipulated endpoint, the attacker secures permanent, persistent access to the victim’s account ecosystem without further user interaction.
Chronology of the Crisis and Industry Fallout
The disclosure timeline highlights a rapidly escalating tension between aggressive AI deployment schedules and enterprise-grade software security validation:
- Late August 2026: Meta officially introduces the Muse ecosystem for macOS, marketing the assistant as a proactive, privacy-centric autonomous agent capable of cross-application workflows and transactions.
- Early September 2026: Meta publishes dual technical whitepapers detailing its safety design methodologies, arriving concurrently with reports of broader industry incidents involving unaligned AI models at competing firms like Anthropic and Google.
- September 7, 2026: Roughly 12 hours before public security disclosures, e-commerce giant Amazon proactively blocks the Muse assistant from interacting with its digital storefront, classifying it as an unauthorized agent violating corporate terms of service.
- September 8, 2026: Security researcher Patrick Wardle publicly details the zero-day vulnerability, demonstrating how basic terminal interactions can bypass security controls and hijack cloud-authenticated sessions.
- November 2026 (Scheduled): Wardle is slated to present a comprehensive technical breakdown of the Muse vulnerability and broader agentic threats at the upcoming Objective by the Sea security conference.
Corporate Stances and the Amazon Blockade
Meta executives and corporate communications representatives have largely declined to address specific technical inquiries regarding the flaw, though the company’s published literature heavily emphasizes privacy-by-design frameworks. These defensive posture publications arrive amid broader technological fallout, following public revelations that internal testing of autonomous models from external developers like Anthropic and Google has occasionally resulted in unintended third-party network breaches.
Simultaneously, commercial friction has materialized outside the security sphere. Approximately half a day prior to Wardle’s public disclosure, Amazon instituted a hard block against the Muse platform, restricting users from attempting to complete retail checkouts or browsing tasks via the assistant. Individuals attempting to leverage the tool encountered automated error dialogs notifying them that Muse constituted an unauthorized artificial intelligence agent in direct violation of standard retail policies.
In an official corporate statement, Amazon emphasized the necessity of transparency and consent within agentic commerce ecosystems. Drawing parallels to established third-party services—such as food delivery platforms coordinating with restaurants or online travel agencies booking airline itineraries—Amazon asserted that autonomous shopping agents must operate transparently and respect the operational boundaries of underlying service providers. Amazon confirmed it had formally requested that Meta excise its platform capabilities from the Muse interface entirely.
Technical Design Flaws and the Debate Over System Security
Security analysts have pointed to foundational design decisions made by Meta’s engineering teams as the root cause of the vulnerability. Most notably, Meta opted to route Muse dictation and transcription processes entirely through cloud-based infrastructure to facilitate centralized logging. Apple’s macOS ecosystem has historically offered native, secure, on-device transcription APIs that retain sensitive audio processing locally without exposing configuration endpoints to local applications. Had Meta utilized these native operating system primitives, the zero-day exploit vector would have been mathematically impossible.
Critics argue that developers of autonomous AI agents often operate under a fundamentally flawed paradigm, assuming that underlying operating system compromises absolve applications of internal security hygiene. Wardle challenges this perspective, noting that the security bar for autonomous agents must be set incomparably higher than traditional software due to the sweeping, high-privilege access these tools demand over personal communications, financial transactions, and sensitive personal data.
Broader Implications for the Autonomous AI Era
The rapid emergence and subsequent compromise of Meta’s Muse assistant highlight a troubling industry trend: the rush to deploy agentic artificial intelligence often supersedes rigorous threat modeling and defensive architecture. As AI agents evolve from passive conversational chatbots into active participants capable of executing financial transactions, modifying local files, and interfacing with secure personal accounts, they inherently become high-value targets for cybercriminals.
The revelation that a simple configuration override can transform a consumer productivity assistant into an automated data-exfiltration utility underscores a stark reality. While technology giants continue to market autonomous agents as secure, private, and seamlessly integrated extensions of the user, the architectural complexity of these systems frequently introduces catastrophic attack surfaces. Unless the technology sector adopts a security-first design methodology that treats AI agents as inherently untrustworthy components, users will remain acutely vulnerable to sophisticated account takeovers, silent data harvesting, and systemic privacy breaches disguised as productivity enhancements.